How-to: Audit Server-Side Encryption and KMS Usage
Use this workflow to inventory bucket default-encryption settings, find unexpected algorithms or KMS key identifiers, and build a remediation queue.
BucketReef currently provides the strongest bulk support for the audit and selection phase. Encryption changes are reviewed and applied from each bucket's configuration rather than through a direct bulk encryption action.
Prerequisites
- Access to Ceph Admin > Buckets.
- The selected endpoint exposes server-side-encryption capability.
- An approved encryption policy, including accepted algorithms and KMS key IDs.
1. Define the expected encryption policy
Before filtering, write down the expected state for each bucket family. For example:
| Bucket family | Expected default encryption |
|---|---|
finance-prod-* |
aws:kms with the production finance key |
research-* |
AES256 or an approved project KMS key |
| public test buckets | documented exception only |
Do not use the audit to infer which KMS key should be selected when ownership or data classification is unclear.
2. Find buckets with unexpected settings
- Open Ceph Admin > Buckets.
- Open Advanced filter.
- Use Server-side encryption detail criteria such as encryption algorithm and KMS key ID.
- Narrow by owner, naming convention, S3 tag, or UI tag to compare like-for-like workloads.
- Repeat the filter for each expected bucket family and record mismatches.
Useful review sets include buckets with no expected algorithm, buckets using
aws:kms with an unexpected key ID, and buckets whose configuration cannot be
resolved because the endpoint does not expose SSE capability.
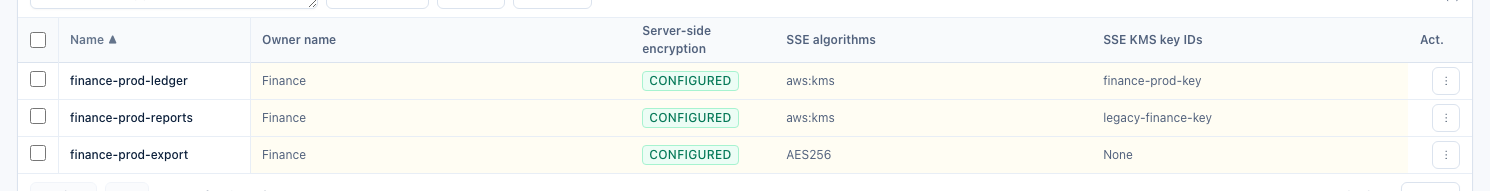
Expose the encryption columns during the review so mismatches are visible in
the working set. The example below separates the expected KMS key, a legacy KMS
key, and an AES256 bucket with no KMS key ID.
3. Tag the findings
Use Actions… > Selection > Manage UI tags… to classify results, for example:
encryption-compliant;encryption-remediate;kms-key-review.
These tags do not alter S3 encryption. They preserve the operator review set inside BucketReef.
4. Review and remediate individual buckets
For each bucket tagged for remediation:
- Open the bucket configuration drawer.
- Review the current default server-side-encryption algorithm and KMS key ID.
- Confirm that the intended KMS key is accessible to RGW and approved for the workload.
- Apply the required bucket encryption configuration.
- Reopen or refresh the bucket and verify the resulting settings.
Work through the tagged remediation set until no unresolved bucket remains.
5. Re-run the audit
- Return to Ceph Admin > Buckets.
- Reapply the same SSE algorithm and KMS-key filters.
- Confirm that all buckets in each family now match the documented policy.
- Keep durable compliance tags only if they are useful for recurring reviews; otherwise remove temporary campaign tags.
Limits / feature flags
Note
Server-side-encryption columns and Advanced filter details follow the endpoint SSE capability. Ceph RGW support for SSE modes and KMS backends also depends on the RGW deployment configuration.
Ceph Admin does not currently expose a direct multi-bucket Set encryption operation in Configure selected buckets…. Keep encryption remediation explicit per bucket.