Workspace: Admin
When to use
Use Admin for platform governance and global configuration.
Prerequisites
ui_adminorui_superadminrole.
Steps
- Open
/admin. - Use Identity & Access to manage UI users.
- Use Managed Tenants to manage RGW accounts and users.
- Use Connections for S3 connections.
- Use Storage Backends for endpoints and endpoint status.
- Use Usage & Metrics to review endpoint-scoped storage, usage composition, usage history, and traffic from tabbed categories.
- Use Audit & Reporting for the effective-access inventory, cost, stored usage-history snapshots, and the control-plane/security audit trail. Object operations are investigated in S3 provider access logs, not Admin Audit.
- If superadmin, use Settings pages for global behavior, authentication options, UI-managed OIDC/LDAP providers, and key rotation.
The RGW Accounts page uses /admin/s3-accounts. The former frontend alias
/admin/accounts is no longer supported; update bookmarks to the canonical
URL. Backend account endpoints under /api/admin/accounts are unchanged.
RGW Accounts and Ceph tenants
RGW Account IDs and Ceph tenants are independent identifiers. BucketReef supports
imported accounts and standalone RGW users in the default tenant or an explicit
tenant. Managed Account and RGW User creation uses the default tenant unless a
super-admin enables Managed RGW tenant creation in General settings
(general.allow_managed_rgw_tenant_creation). The option is disabled by
default and gates both managed creation and tenant-aware imports. Ceph Admin can
always create an Account or User in an explicit tenant.
To import an account, enter one Account ID per line. The importer preserves the
tenant returned by RGW and discovers its existing account root, including custom
root UIDs. You may append an existing root UID after a space, for example
RGW12345678901234567 customer01$customer01-root. This also avoids enumerating
the user inventory when the root is already known. The selected root must belong
to the imported account and tenant.
For standalone users, import either uid for the default tenant or, when
Managed RGW tenant creation is enabled, tenant$uid. Account imports read
the tenant from RGW and may optionally assert the expected tenant through the API.
When the setting is enabled, the Account and RGW User create forms also accept
an optional tenant. Namespaces remain scoped by endpoint,
tenant and UID, so the same UID can be imported from different tenants. The
stored tenant is read-only after import or creation. Portal continues to require
an RGW Account and personal IAM identities; standalone RGW users are
Manager/Browser contexts.
Statistics, traffic, quotas, keys, physical bucket tags and usage-history collection retain the selected tenant. S3 and IAM requests use the selected principal's credentials, with RGW enforcing the implicit tenant. BucketReef does not change tenant lifecycle or migrate identities between tenants.
Expected result
Platform and tenant-entry resources are configured and auditable.
Reading the overview
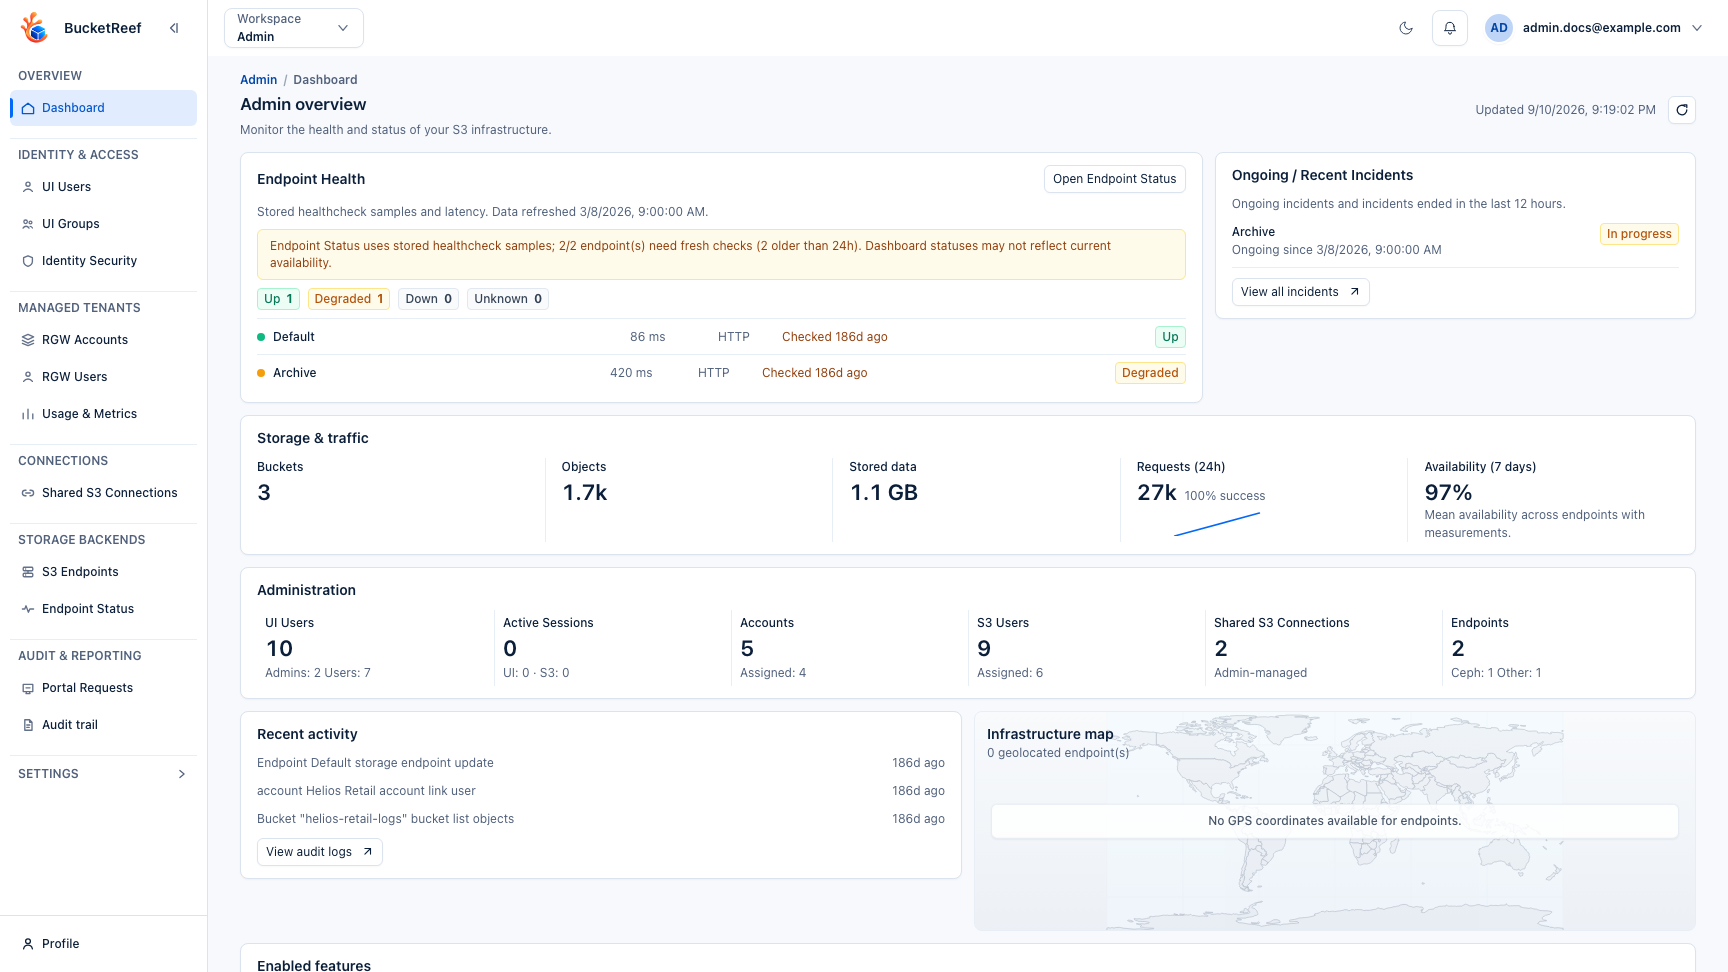
Start with Endpoint Health and Ongoing / Recent Incidents. Endpoint rows show the name, latency, check mode, time of the last check and stored status. The first eight endpoints are shown; Open Endpoint Status and View all incidents lead to the detailed monitoring page. Warnings describe missing or old healthcheck samples: refreshing the dashboard retrieves stored data and does not run a new healthcheck.
Storage & traffic aggregates the Ceph endpoints managed and supervised by BucketReef. An endpoint is included when its Supervision identity is ready with complete credentials and Metrics or Usage is enabled. Both managed and externally provisioned Supervision identities are included; the default endpoint has no special role. Measurements cover only the Accounts and S3 Users registered in BucketReef on each endpoint, not every tenant on the Ceph cluster.
Bucket and object counts and stored data use endpoints with Metrics enabled. Requests for the last 24 hours use endpoints with Usage enabled; the success rate is calculated from the combined successful and total requests. Only requests have a trend line, and only when samples exist. Seven-day availability is the mean across endpoints in the union of those two groups with healthcheck measurements; it is not a live health score. Endpoint Health, incidents and the infrastructure map continue to cover the global endpoint inventory.
The card keeps a short Managed & supervised Ceph scope label beside the metrics. The i next to its title opens details on hover, keyboard focus or click; press Escape or click outside to dismiss it. These details show separate endpoint coverage for Storage, Traffic and Availability, collection dates and the aggregation and cache rules. Storage coverage counts endpoints with all three measurements complete. Available partial totals stay visible with compact Storage partial, Traffic partial or Availability partial badges; notes in the tooltip identify endpoints with missing measurements or failed collection. Missing values appear as a dash, while a measured zero stays zero. An empty eligible group explains the required Supervision credentials and feature configuration. Storage, traffic and health load independently.
Storage and Traffic results are cached for up to 30 minutes in memory in each backend process. Opening the dashboard or pressing Refresh reuses these results without contacting RGW again. The first request after expiry collects new data; concurrent requests share that collection. The information tooltip displays the Storage collection date and the end of the Traffic window, while the header's Updated date is the last dashboard retrieval. Cached reads preserve the original 24-hour window.
Complete results, partial results with at least one contributing endpoint, and an empty eligible group are kept for 30 minutes. A completely unavailable collection is kept for only 60 seconds to allow a faster retry. The current endpoint and tenant scope is checked in the database on every request; changes to eligibility, RGW configuration, Supervision credentials or registered Accounts/S3 Users invalidate the corresponding cached result. Each process has its own cache, lost on restart; no credentials are stored in cache keys or values. Endpoint scope, health and the Usage & Metrics page retain their existing retrieval behavior.
The Administration band keeps six shortcuts and their aggregate counts, including the UI/S3 session split. Recent activity and the infrastructure map follow, with enabled core and extra features at the bottom. The map stays visible when Endpoint Status is enabled; endpoints without coordinates do not produce invented locations. Long names and event descriptions wrap.
When setup has not been dismissed, its checklist remains above the overview. A completed checklist starts collapsed; Review, Collapse checklist and Dismiss retain control over its display.
S3 endpoint inventory
Open Storage Backends > S3 Endpoints to compare names and URLs, providers
and regions, connection settings, and enabled services. Search matches names,
S3 URLs, providers, regions and tags across the complete inventory. Use ~ for
contains, = for exact matching, or select a provider. Clear all resets the
filters; they remain in place when returning from an endpoint or refreshing its
listing after an action.
Click a row or Edit/View for the existing Connection, Credentials
and Capabilities & health tabs. The table shows at most two tags and three
enabled services; +N indicates additional values available on that page.
Service badges describe configuration; use Endpoint Status for measured
health. Disabling TLS verification is explicitly highlighted.
Set as default, Edit/View and Delete stay visible where applicable. Protected endpoints allow consultation and may still be selected as default; environment-managed configuration and ordinary Admin users remain read-only. Superadmins retain the existing ability to edit tags on protected or environment-managed endpoints. If the management mode cannot be loaded, changes remain unavailable until Retry succeeds. Deletion requires confirmation and a failed operation is not retried automatically.
Endpoint configuration
The three tabs share one draft and one save action. Connection contains identity, tags, provider, TLS and location; Credentials separates Admin Ops, Supervision Ops and dedicated Ceph Admin keys; Capabilities & health contains service configuration and probe settings. Required-field errors open the relevant tab and focus the first invalid field. Enter submits the form. Cancel, navigation and browser history protect unsaved changes; controls remain locked during saving.
Existing secret values stay hidden. A blank secret during editing retains the stored value, and credential-check failures remain advisory. AWS addresses are derived from the region. Read-only configuration remains selectable, while superadmins can still save endpoint tags where allowed.
Configuration and tags are saved separately. When configuration succeeds but tags fail, the page explains the partial result and keeps the tag draft. Retry uses the saved endpoint identity and does not repeat unchanged configuration or create a duplicate endpoint. A tag-only edit does not rewrite configuration.
Editing an RGW account
Open Edit from Managed Tenants > RGW Accounts. General groups tags,
observed usage and quota fields. Usage and saved limits describe the current
configuration; editing a quota does not apply it until Save changes.
Leave a quota value empty to remove that limit. Unchanged quotas are not sent
again when saving tags or associations. Quota controls require verified
accounts=write permission on the endpoint; a failed permission check provides
Retry permissions.
Linked UI users and Linked UI groups use the same searchable picker. Select principals and their roles, then use Add selected to add them to the account draft. Saving reminds you to finish any pending selection. A catalogue loading error provides Retry without hiding existing links. The Advanced association dialog applies its setting to the account draft; save the account to persist it.
Manager features separates optional BucketReef access-key extensions from privileged Ceph operations. Access-key extensions contains the opt-ins for access-key names and notes and access-key expiration. Privileged Ceph operations contains grants such as bucket quota management that require delegated Ceph/RGW administrative capabilities. RGW Users use the same grouping; their privileged operations also include Ceph S3 User key management and managed private connection provisioning. Portal settings, when available, has its own save action: saving either form preserves unsaved changes in the other. While either save is running, fields, tabs and return controls are locked. A failed save keeps the draft for retry. Returning to the account list or leaving the page asks for confirmation when unsaved changes remain.
Compact identity associations
The Managed Tenants RGW Accounts and RGW Users lists, together with Shared S3 Connections, display linked UI users and UI groups as one compact avatar stack. User avatars are circular; group pictograms use a rounded-square shape so the two principal types remain distinguishable. Hover the stack, or focus one of its links with the keyboard, to open a readable panel containing each user email, group name, and role as compact badges. To keep very large tooltips readable, the list is limited to 20 entries and reports how many additional principals remain. Click a user or group pictogram to open that principal directly in its edit page. Emails remain searchable even though they are no longer printed in each row.
The UI Users and UI Groups lists summarize storage associations with
three count badges: RGW accounts, RGW users, and shared S3 connections. Their
hover/focus panel exposes the complete bounded list and its roles. UI Groups
also shows up to five member avatars before a +N indicator; the same panel
still exposes up to 20 members.
The UI User editor uses Profile and preferences and Security, matching the personal profile. Profile and preferences includes identity, avatar, language and quota email preferences. Global quota watch is available only for administrator accounts. Language and alerts are saved with the user form; the avatar has an independent Edit dialog and Save action. Saving an avatar preserves pending changes to identity, preferences and access. Browser-local preferences remain in the personal profile. Admin profile operations follow the same target-role restrictions as other UI User edits.
UI User and UI Group editors group operational workspace access, Manager permissions and Browser options in the Workspaces tab. The three sections share the principal's existing draft and Save action. UI User controls describe direct access; UI Group controls describe permissions inherited by eligible members.
In the UI user and UI group editors, association tabs first list the currently linked resources. Use Add… to open a searchable picker, confirm the pending selection with Add selected, and use Remove on an existing row to unlink it before saving. Each RGW account association has two independent access controls, also available when linking users or groups from RGW Accounts:
- Manager: No Manager access or Account administrator.
- Portal: No Portal access, Portal user, or Portal manager.
Choose at least one role before saving. Both can be granted on the same link: for example, Account administrator together with Portal user grants Manager administration and ordinary Portal membership, not Portal management. Use Remove to unlink the account instead of saving two absent roles. Direct and group grants combine independently for each workspace; removing a direct grant does not revoke an equivalent right inherited from a UI group.
Use Review access from the UI Users, UI Groups, RGW Accounts, RGW Users, and Shared S3 Connections lists to open Audit & Reporting > Access audit with the corresponding context filter. The audit shows the saved result after direct and inherited grants are combined, with a global searchable inventory and CSV export. For UI Groups, the context selects rows to which that group contributes at least one effective right. This authorization review covers BucketReef UI rights; storage-side IAM policies, bucket policies, and S3 ACLs remain outside its scope.
New links initially select Portal user with no Manager access when Portal is enabled, or Account administrator with no Portal access when it is off. Review this choice before adding the link. Disabling Portal makes its controls unavailable or read-only, but preserves stored Portal roles; it never converts them into Manager roles.
Manager's embedded Browser additionally requires Allow Manager Browser data access on the same account association as Account administrator. That advanced opt-in does not grant standalone Browser or Portal access.
Shared S3 Connections are Admin-managed, shared, and Manager-only. Their normal
forms do not expose sharing, Manager, or Browser flags. A connection migrated
without Manager access is shown as Remediation required and must be enabled
with the explicit remediation action. Admin routes return 404 for private
connection IDs; private connections remain owned and managed only from the
owner's profile.
The Portal requests requester badge uses the same avatar and role panel and opens the requester's UI user edit page when that user still exists.
The Created by column of Shared S3 Connections uses the creator's user avatar and exposes the creator identity on hover.
UI group pictograms are managed from Platform > UI Groups > General. A group can use initials, one of the predefined pictograms, or a custom PNG/JPEG image up to 1 MiB. Group images never use Gravatar or an OIDC profile image.
Limits / feature flags
Note
Cost, Endpoint Status, Portal, and some browser settings are visible only when corresponding features are enabled.
Note
UI User role and entitlement rules:
ui_none: no workspace access (profile remains accessible).ui_user: non-admin workspaces only.ui_admin: user-level workspace access plus/admin.ui_superadmin: admin access plus/admin/*-settings.ui_superadminrole assignment/promotion is restricted to superadmin users.can_access_ceph_admincan be granted only by superadmin users, and only forui_adminorui_superadmin.can_access_storage_opscan be granted byui_adminorui_superadminforui_user,ui_admin, orui_superadmin.- Manager access can be configured by
ui_adminorui_superadminfrom the Manager tab. Each tool also requires its matching global Manager setting to be enabled. - Manual private S3 connection creation is configured from the Connections tab. Managed IAM/RGW provisioning is configured from the Manager tab. Both rights are direct or inherited from UI groups.
- Entitlements are automatically disabled when the target role does not support them.
Note
Admin Settings > Authentication manages access-key login options and UI-defined OIDC/LDAP providers. OIDC and LDAP providers defined by backend environment variables are visible there but remain locked/read-only.
Related pages
- Feature: Endpoint Status in Admin
- Feature: Cost in Admin
- Feature: Admin Usage and Metrics
- Feature: Usage History in Admin
- Feature: Key Rotation in Admin
- Admin: Effective Access Audit
- Admin: Audit
- Storage admin runbook
- Workspace: Manager
- Ops / Configuration
- Ops / Security
Visual example
Editing platform settings
General, Authentication, Browser, Manager and Portal settings use compact sections with one Save changes / Cancel area that appears after an edit. Reset to defaults loads defaults for the current page into its draft; review them and save to apply them. Other settings pages are preserved. Concurrent edits to the same field are reported instead of overwritten.
General contains workspace availability, services, quota alerts and branding. Configure SMTP opens an internal draft with an explicit test-email action; testing does not save that draft. Apply copies dialog values to the page. The branding preview is local until a successful save updates the interface. Manager migration limits and Portal CORS origins use the same dialog pattern.
Authentication lists external providers separately from the global login and security policy. Add, Edit and View open dedicated OIDC/LDAP pages with compact Identity and Connection sections. OIDC adds sign-in options, protocol security and identity linking; LDAP adds user search, identity mapping and transport security. Save provider / Cancel stays reachable at the bottom of the page. Provider saves are independent of policy saves.
Environment-managed values stay locked and explain their source; consultation shows Close instead of Save. Existing secrets are never displayed. Leave a replacement empty to preserve the stored secret. OIDC offers an explicit Clear stored client secret acknowledgement. Removing the LDAP Bind DN and leaving the password empty switches to anonymous search and removes the stored bind password when saved.
Leaving with unsaved changes asks whether to keep editing or discard them. Failed saves keep the draft for retry, and a failed provider load offers Retry before editing becomes available. Saving, including any requested passkey verification, temporarily locks the form and navigation.
These administration pages remain in English. The user Portal project settings and shared profile support English, French, German and Simplified Chinese.